Signal has fixed a vulnerability that could, in certain cases, prevent calls from ending properly on Android.
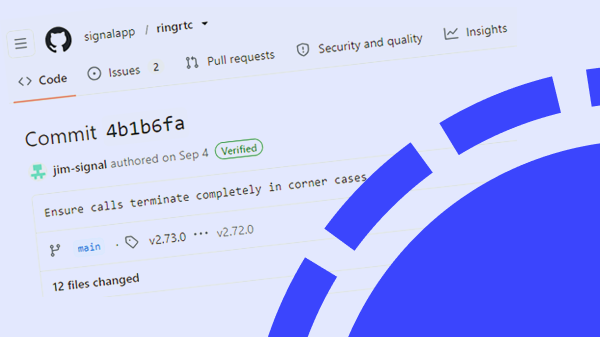
The issue, tracked as CVE-2026-113380, is caused by a flaw in RingRTC, the open-source library used for Signal’s voice and video calls. According to a Signal spokesperson, the bug could only be reproduced in Signal for Android. To exploit the flaw, an attacker would first need to be participating in a call with the victim. The attacker could then overload the system’s event queue, potentially causing audio and possibly video to continue after the other person hangs up.
However, Signal’s message request system automatically blocks calls from unknown contacts, meaning random attackers could not have exploited this bug. An attacker would first need to have had a message request accepted by the victim or be in a group chat with them before they could call the victim. This protection has been part of Signal for many years.
The vulnerability affects RingRTC versions earlier than 2.72.0, although the reported behavior was only reproducible on Android. There are no known reports of the flaw being exploited in the wild. Even if the vulnerability were exploited, Android displays indicators in the status bar when an app is using the microphone or camera, which may help users notice unexpected activity.
The fix was included in the 8.27 update for Signal Android, which started rolling out on September 9th, 2026. Following its usual weekly release schedule, Signal Android has since been updated to version 8.33. While this bug only affected Android, always keep Signal up to date on all your devices to benefit from the latest security improvements and new features.
Stay Informed
Want to stay up to date with the latest Signal news, tips, and updates? Follow us on Bluesky or Mastodon.